Atlassian’s CVE-2026-21589 affects eight self-hosted Data Center products and allows unauthenticated access to known files in the web…
At an October 6 hearing, OpenAI and Anthropic said they would accept mandatory disclosure of serious AI-agent incidents.…
DTU says attackers used compromised profiles to reach its DTUBasen identity system and download a large amount of…
Cisco says CVE-2026-76504, an actively exploited CVSS 9.8 API authentication-bypass flaw in Catalyst SD-WAN Manager, can grant unauthenticated…
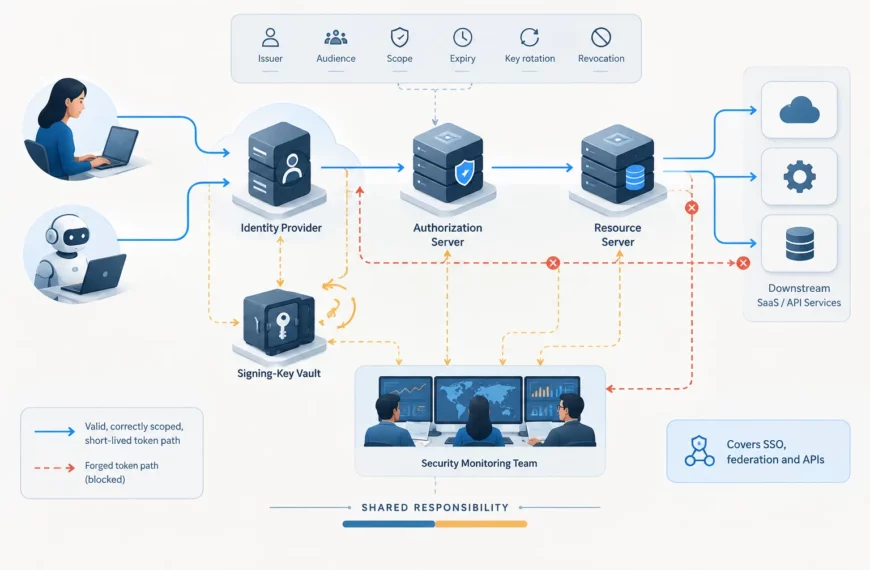
LiteLLM’s official 1.107.0 release was hijacked through exposed secrets and stolen GitHub tokens, then distributed through the project’s…
eMudhra says it will leave the public SSL/TLS market after weak intermediate CA keys led browsers to distrust…
 By
 By
 By

 By
 By